Policies
Access is denied by default. A database policy grants named console users access to one database, as one database user, with specific privileges - and decides whether each login needs MFA.
Create a Policy
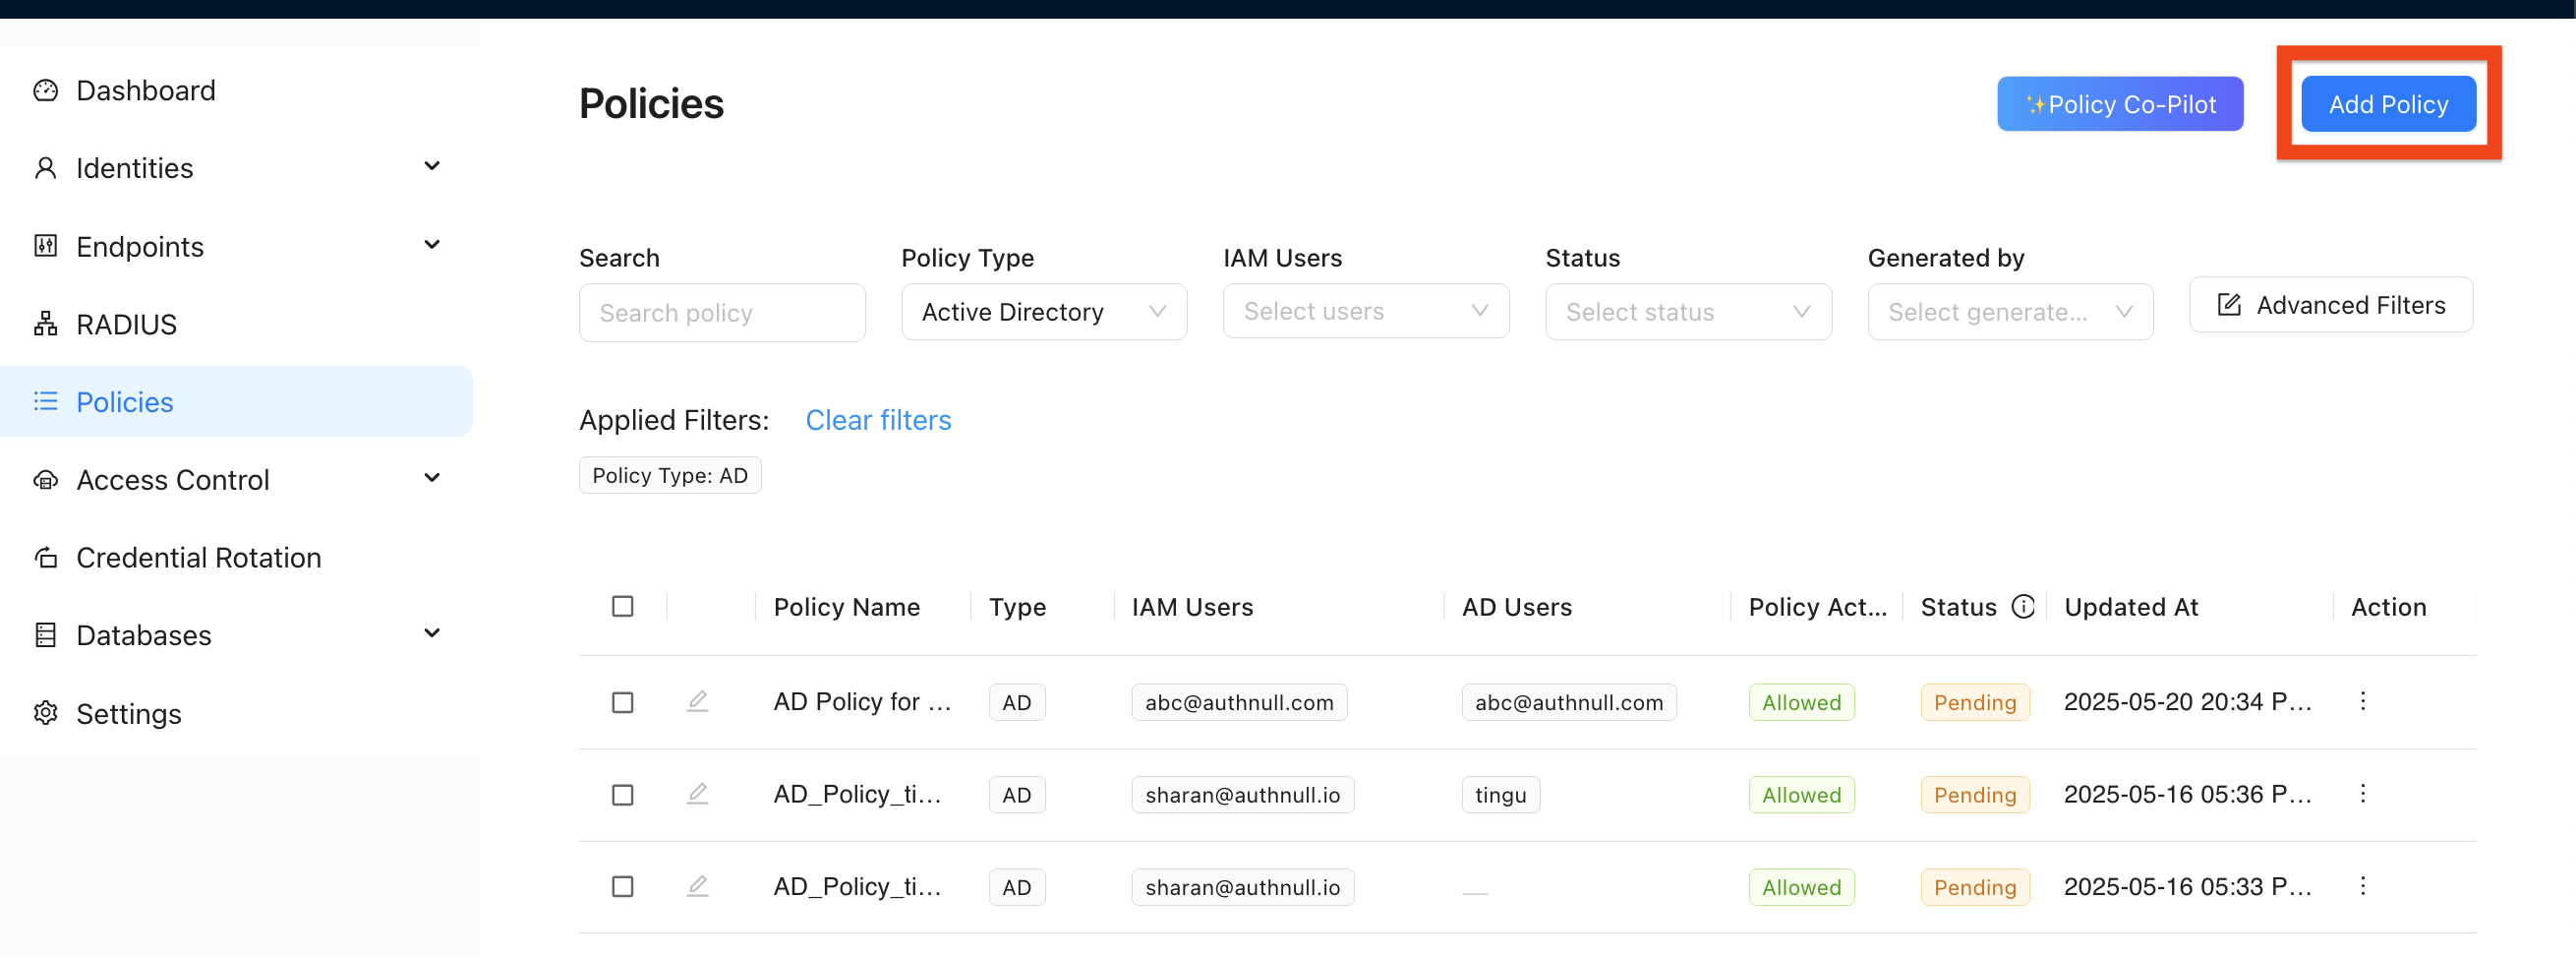
Go to Policies and create a database policy.
| Field | What to choose |
|---|---|
| Policy name | Any name, for example db-access-policy |
| Database Host | The database server, from those the agent has discovered |
| Select Database | The database on that server |
| Database User | The database role users will connect as. The agent manages its password |
| Privilege | READ, WRITE, and/or EXECUTE |
| Fields to mask | MySQL only: columns to mask in query results, per table |
| Select IAM Users | The console users who may use this access. They receive the push |
| Action | What happens when they connect: Require MFA, Allow, or Block |
| Action | Effect |
|---|---|
| Require MFA | The user approves a push before every login |
| Allow | The login proceeds without MFA |
| Block | The login is refused, and no push is sent |
All tables in the database are covered; the privileges apply to each of them.
What Happens Next
Creating the policy queues a job for the agent. On its next sync (within a minute) the agent sets a new password on the database role and adds the user to ProxySQL. To confirm:
sudo grep -E 'created successfully in ProxySQL|updated successfully in ProxySQL' /var/log/authnull-db-agent.log | tail -3
The policy is active as soon as it is created.
Manage Policies
The Policies screen lists every database policy, with filters for database and status. A policy's ⋯ menu offers:
| Action | Effect |
|---|---|
| Update policy | Change the users, privileges, or action. Saving also queues a new job, so the agent provisions the user again |
| Pause | The policy stops applying until it is Re-activated |
| Revoke | Withdraw the access |
| Approve | Shown only for a policy that is not yet approved |
Next Steps
Continue to Connecting to open a session.